Sevita single sign on lets team members sign in once and reach multiple work apps instead of juggling separate passwords. SSO works through an identity provider that verifies you, usually with multifactor authentication. Sevita has not published an official public SSO manual that I could verify, so confirm your portal link and sign in method with your IT service desk.
Key Facts at a Glance
Who Sevita is: formerly The MENTOR Network, founded in 1967, with about 40,000 team members supporting 50,000 individuals in 40 states, per Sevita's own announcement.
What SSO does: it lets you sign in to multiple apps using a single authentication flow.
Common protocols: Okta supports SAML 2.0 and OpenID Connect.
Best MFA guidance: CISA strongly urges phishing resistant MFA (October 31, 2022).
Identity standard: NIST published SP 800-63-4 Digital Identity Guidelines in 2025.
What Is Sevita Single Sign On?
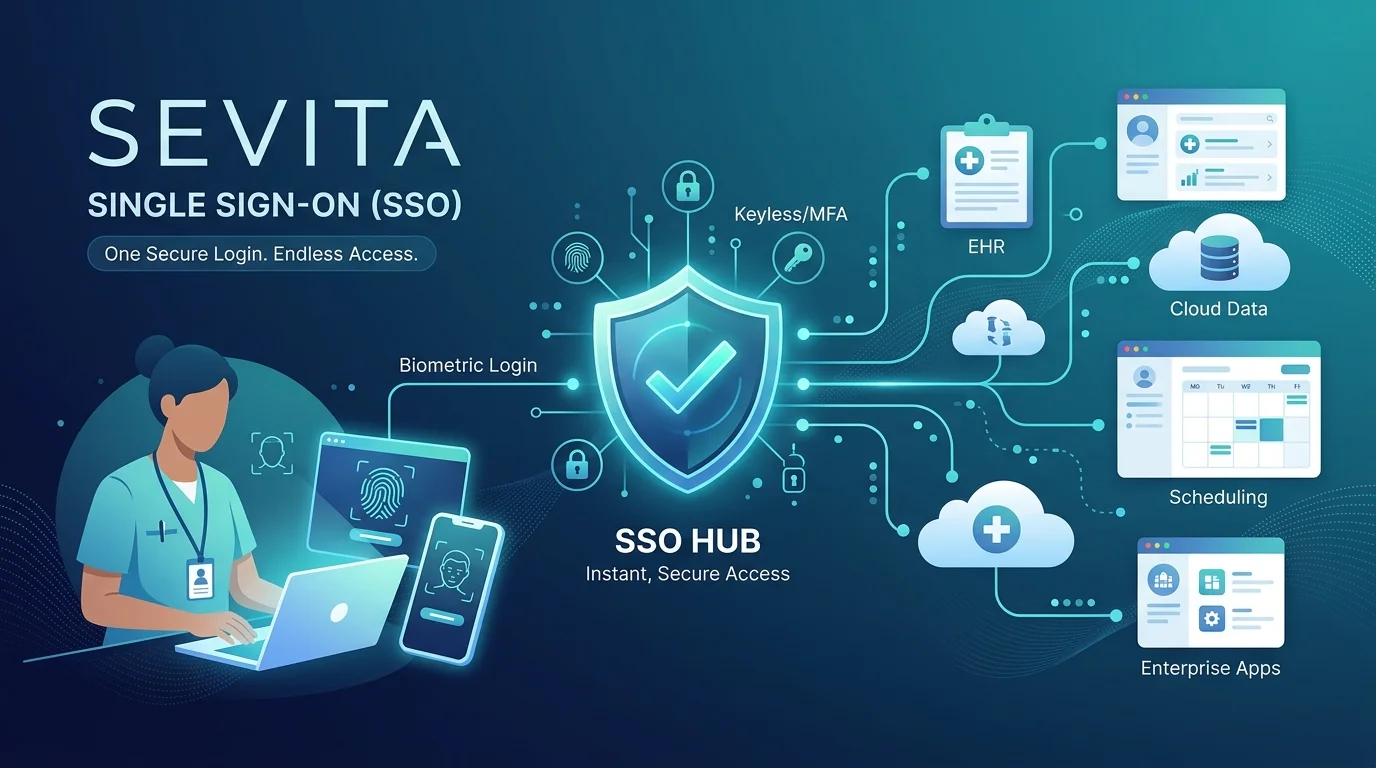
Sevita single sign on is the one login approach that lets a team member reach multiple work tools after verifying once. Sevita supports people across home and community based care, so staff need quick, secure access to many systems.
Here is the catch. Many websites describe Sevita's exact SSO setup, but they are unofficial and often contradict each other. So I am sticking to what is verifiable: how SSO works and how to use it safely.
Why Does SSO Matter in Healthcare?
SSO matters in healthcare because every login can be a doorway to protected health information (PHI). HHS explains that authentication is the prerequisite for letting only authorized people into systems and data.
The HIPAA Access Control standard (§164.312) is a technical safeguard for electronic health records. Good SSO supports it. Here is what you gain:
Fewer passwords, so less password fatigue and fewer reset tickets
Centralized access control in one place
A cleaner audit trail for compliance reviews
Faster user provisioning and deprovisioning, which Okta supports
How Does Single Sign On Work?
SSO works by sending you to a central identity provider, which verifies you and then vouches for you to each app. The app gets a signed message, called an assertion, confirming who you are.
NIST describes this as federation: one provider supplies authentication information to separately run systems. The table below compares the usual options.
Method | What it is | Best for |
|---|---|---|
Basic sign in | Separate username and password per app | Small setups with few apps |
SAML 2.0 | XML based assertions between an identity provider and an app | Enterprise and legacy web apps |
OpenID Connect | Modern, token based sign in layer | Cloud and mobile apps |
Behind the scenes, your browser should also trust the portal you are visiting. If you are curious how that trust is built, here is a plain explainer on the SSL certificate chain.
How Do You Log In Step by Step?
You log in by opening your official portal, entering your work credentials, and approving MFA. Do not use a search result or an emailed link to get there. If you are working off network, your organization may also require a VPN, and it helps to understand what an IPsec VPN is before you call the help desk.
What should you do before logging in?
Get your recovery options sorted first, because account lockout is a common headache.
Confirm your work email and username with your supervisor.
Install the authenticator your organization requires.
Bookmark the official portal link from your IT team.
What does the login flow look like?
Open your approved portal in an updated browser.
Enter your work email or username.
Complete your multifactor authentication prompt.
Launch your apps from the dashboard without signing in again.
What if the login fails?
Check your connection, try a private browser window, then contact the IT service desk. Repeated failed attempts often cause lockouts.
Which MFA Method Is Safest?
Phishing resistant MFA is the safest option, according to CISA. If you use push notifications, CISA recommends number matching as an interim fix against MFA fatigue.
MFA type | Strength | Notes |
|---|---|---|
SMS or voice codes | Weaker | Exposed to SIM swap and interception |
Push notification | Moderate | Vulnerable to repeated prompt attacks |
Push plus number matching | Stronger | CISA's recommended interim step |
FIDO/WebAuthn or PKI | Strongest | Phishing resistant; a hardware network security key is one example |
Your part is simple: never approve a prompt you did not trigger, and watch for fake "verify your login" emails. Credential stealing malware matters too, so learn what a keylogger is and how to avoid one.
Frequently Asked Questions
What is Sevita single sign on?
It is a one login system that lets team members reach multiple work apps after verifying once.
What is the official Sevita SSO login URL?
I could not verify one from official sources. Ask your IT service desk for the approved link rather than trusting third party sites.
Does Sevita use Okta or Azure AD?
Unofficial sites claim both, but I could not confirm either from Sevita directly. Your IT team can tell you.
Is SSO secure?
Yes, when paired with strong MFA. One login opens many apps, so that login must be well protected.
Is SSO required by HIPAA?
No. HIPAA requires access control and person or entity authentication, but it does not mandate SSO or a specific MFA product.
What should I do if I am locked out?
Wait the recommended period, then contact the IT service desk. Do not keep retrying.
What is the safest MFA type?
Phishing resistant MFA, such as FIDO/WebAuthn, per CISA.
Should You Adopt Single Sign On?
Yes. SSO paired with strong MFA is one of the most practical ways to improve identity and access management while saving staff time. You cut password chaos, tighten security and simplify audits.
If you are a Sevita team member, confirm your portal, MFA method and recovery options with your IT service desk this week. If you run an organization, choose an SSO and MFA solution built on open standards like SAML and OpenID Connect, and roll it out in phases.